TL;DR

Prime made for students and young adults
- Fast, free delivery for dorm and study essentials
- Prime Video and Amazon Music included
- Member-only deals
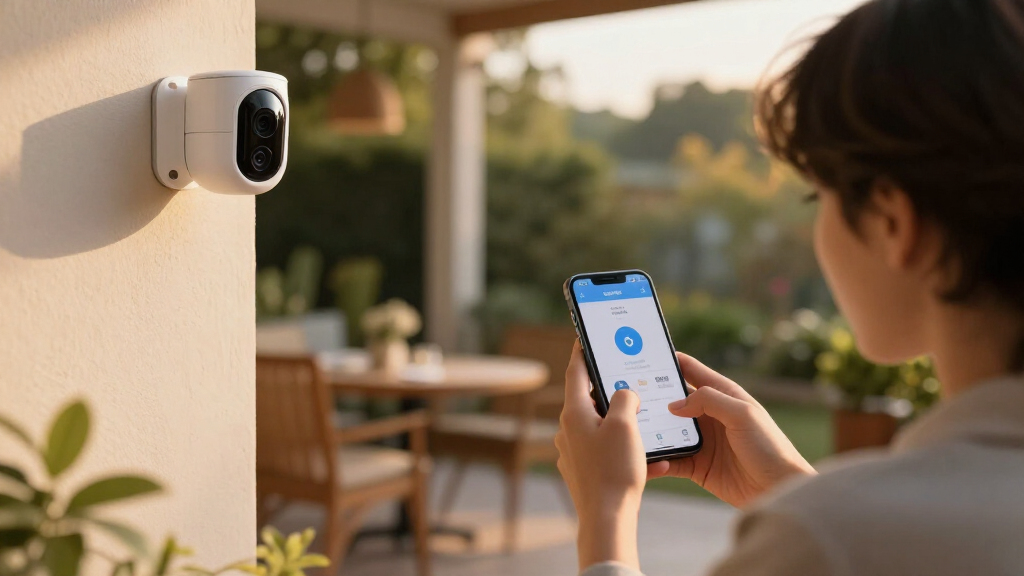
A security researcher discovered that certain security cameras transmit admin tokens in their login pages, potentially exposing sensitive data. The issue is confirmed through testing, but the full scope remains unclear. This raises questions about device security and data privacy.
A recent security assessment has confirmed that some security cameras transmit admin tokens in their login pages, posing a potential risk of sensitive data exposure. This discovery is significant for organizations relying on these devices for security, as it could enable unauthorized access if exploited.
The investigation, conducted by cybersecurity researchers, revealed that certain models of security cameras include admin tokens within the login interface, which are typically used for device management and authentication. These tokens, if accessible, could allow malicious actors to gain control over the devices or access sensitive data.
While the specific models affected are still being identified, initial tests confirmed that at least some cameras shipped with tokens embedded directly in the login page’s source code or network traffic. Experts warn that this could be exploited if attackers intercept or access device communications, especially on unsecured networks.
Manufacturers have yet to issue official statements or security advisories regarding this issue, and it is unclear whether the problem stems from a software bug, misconfiguration, or a deliberate design choice. Ongoing investigations aim to clarify the scope and severity of the vulnerability.
Implications for Device Security and Data Privacy
This discovery matters because it exposes a potential vector for attackers to compromise security camera systems, which are increasingly integral to organizational and personal security. If malicious actors access admin tokens, they could manipulate camera feeds, disable devices, or access connected networks, leading to data breaches or physical security risks.
For small and mid-sized organizations, such vulnerabilities could be exploited without sophisticated hacking skills, especially if devices are connected to unsecured networks. The issue underscores the importance of scrutinizing device security features and ensuring proper network protections.
Popular right now

Apple AirPods Pro 3 Wireless Earbuds with Active Noise Cancellation

Dyson V8 Cyclone Cordless Vacuum

Dreame L40 Ultra Gen 2 Robot Vacuum and Mop
As an affiliate, we earn on qualifying purchases.
Security Camera Vulnerabilities and Past Incidents
Security cameras have historically been targeted for various vulnerabilities, including weak default passwords, unsecured network access, and firmware flaws. Previous incidents have demonstrated how attackers can hijack devices for surveillance, espionage, or as part of botnets.
This recent finding adds a new dimension by showing that sensitive authentication tokens may be transmitted insecurely, increasing the risk of remote compromise. Experts have long warned that IoT devices often lack robust security measures, and this case highlights ongoing challenges in device design and security oversight.
“Some security cameras are transmitting admin tokens openly in their login pages, which could be intercepted by attackers.”
— an anonymous cybersecurity researcher
Scope and Impact of the Token Exposure
It is not yet clear how widespread this issue is across different brands and models of security cameras. The full extent of potential exploitation and whether current firmware updates mitigate the problem remains under investigation. Details about whether the tokens are accessible remotely or only locally are still emerging.
Ongoing Investigations and Manufacturer Responses
Researchers are continuing to identify affected devices and assess the severity of the vulnerability. Manufacturers are expected to review their firmware and security protocols, with some possibly releasing patches or advisories. Security teams should monitor updates and consider reviewing device configurations for exposed tokens.
Further testing and industry disclosures are anticipated in the coming weeks to clarify the scope and mitigation steps for this issue.
Key Questions
Could this vulnerability allow attackers to access my security camera remotely?
Yes, if the admin tokens are accessible and not properly secured, attackers could potentially use them to gain remote control over affected devices.
Are all security cameras affected by this issue?
It is currently unclear how many models are impacted. Ongoing investigations aim to determine the full scope of the problem.
What can organizations do to protect their devices now?
Organizations should review device configurations, ensure firmware is up to date, and consider network segmentation to limit exposure until patches are available.
Will manufacturers issue security updates for this vulnerability?
Manufacturers have not yet issued official statements, but updates are expected as the scope becomes clearer.
How serious is this vulnerability compared to other IoT security issues?
This vulnerability is significant because it involves sensitive authentication tokens, which could enable full device compromise if exploited.
Source: IdeaNavigator AI