📊 Full opportunity report: Top Challenges In Securing Remote Devices And How To Overcome Them on IdeaNavigator AI — validation score, market gap, and execution plan.
TL;DR
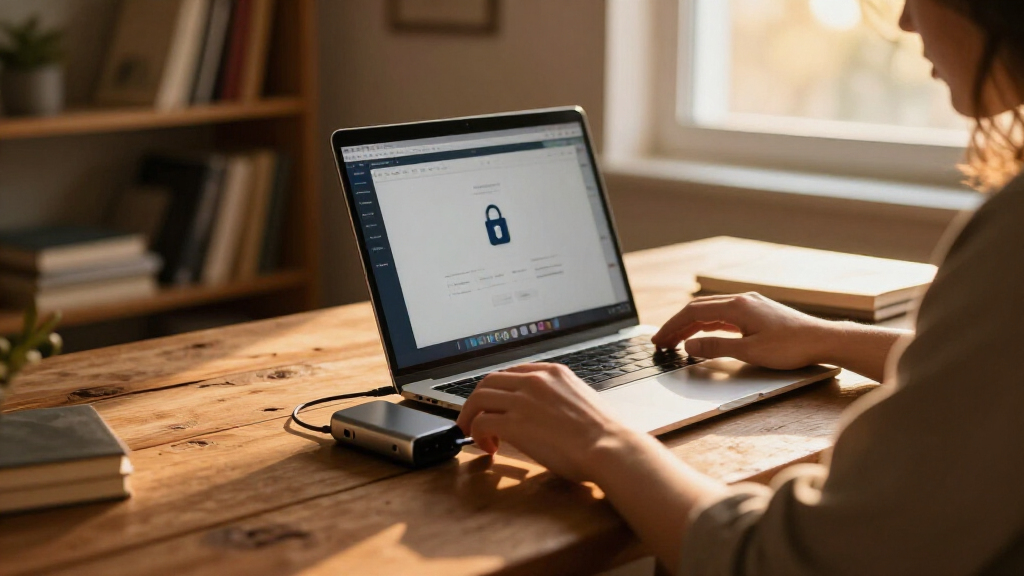
Remote device security faces significant challenges, including unmanaged hardware and compliance gaps. New lightweight tools aim to improve posture verification without invasive controls, helping SMBs meet security standards.
Security challenges in managing remote devices are intensifying as organizations face increasing compliance requirements and diverse hardware environments. A new approach involves deploying lightweight, voluntary agents to assess device security postures without invasive management tools, offering a practical solution for SMBs with employee-owned hardware. This development addresses a critical gap in verifying security compliance across mixed-device fleets.
Organizations with remote teams often struggle to verify the security status of personal and unmanaged devices, such as outdated Windows laptops, MacBooks, and smartphones. These devices frequently lack essential security features like disk encryption, timely OS updates, or screen locks, creating vulnerabilities that can lead to data breaches or compliance violations.
Traditional Mobile Device Management (MDM) solutions are often too invasive or incompatible with employee-owned devices, leaving a verification gap. In response, a new minimal-agent approach has emerged, allowing employees to voluntarily install a lightweight security checker that assesses key security parameters such as encryption status, OS update level, screen lock activation, and password manager presence. The tool reports pass/fail results to a centralized dashboard, enabling security teams to monitor compliance without remote control or intrusive management.
Market validation involves deploying this solution at small startups facing SOC 2 audits, measuring device enrollment rates, and ensuring auditors accept the generated posture reports as sufficient evidence of security compliance. The business model relies on per-device monthly pricing, with additional features like compliance report exports available on paid tiers. This approach aims to improve security posture verification for SMBs managing diverse, employee-owned hardware in a cost-effective, minimally invasive manner.
Why Securing Remote Devices Is Critical Now
The rise of remote work has expanded the attack surface for organizations, making it essential to verify that all devices accessing corporate data meet security standards. Failing to do so can result in data breaches, regulatory penalties, and damage to reputation. The new lightweight, voluntary agent approach addresses a key compliance gap, enabling SMBs to better manage risks without the drawbacks of traditional MDM solutions. As regulatory scrutiny increases and customer trust becomes paramount, effective remote device security verification is more important than ever.
lightweight device security checker
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Remote Work and the Growing Device Security Gap
Over the past few years, the shift to remote work has led to a proliferation of employee-owned devices used for work purposes. Many of these devices are unmanaged, outdated, or lack basic security controls, which complicates compliance efforts, especially under frameworks like SOC 2. Conventional MDM solutions, while effective for corporate-owned hardware, are often too invasive or incompatible with personal devices, creating a verification challenge for security teams.
Recent market developments include the emergence of lightweight, voluntary agents designed specifically for remote device posture assessment. These tools aim to fill the gap by providing a non-invasive way to verify encryption, OS updates, and other security controls, aligning with compliance requirements without infringing on employee privacy or autonomy. Early deployment trials at SMBs show promise, but widespread adoption and acceptance by auditors are still developing.
remote device compliance verification tools
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Unverified Effectiveness and Adoption Challenges
While initial deployments are promising, it remains unclear how widely these lightweight agents will be adopted across different industries and organizational sizes. Questions persist about whether auditors will accept these posture reports as sufficient evidence for compliance, and whether employees will consistently voluntarily install and maintain these tools. Further validation and broader testing are needed to confirm their effectiveness and integration into standard security workflows.
employee-owned device security software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Next Steps in Deploying Remote Device Security Tools
Organizations planning to adopt these lightweight security checkers should pilot the tools within their teams, focusing on device enrollment rates and audit acceptance. Further research is expected to refine the agent’s capabilities and improve user experience. Industry-wide, broader validation and potential regulatory recognition will determine whether these tools become standard practice for remote device security verification. Continued engagement with auditors and security standards bodies will also influence their adoption.
As an affiliate, we earn on qualifying purchases.
Key Questions
How do lightweight security checkers differ from traditional MDM solutions?
They are voluntary, non-invasive tools that assess security posture without remote control or intrusive management, making them suitable for employee-owned devices.
Will these tools be accepted by auditors for compliance evidence?
Acceptance is still under review; early deployment trials aim to demonstrate their reliability, but broader validation is needed for widespread recognition.
What security parameters do these agents check?
They assess disk encryption, OS update status, screen lock activation, and password manager presence.
Are there privacy concerns with voluntary device checks?
Since these are non-invasive, privacy concerns are minimized; the focus is solely on security posture rather than personal data.
What happens if a device fails the security check?
Employees receive self-remediation instructions, and security teams can monitor compliance without remote control interventions.
Source: IdeaNavigator AI